
hacker, sec engineer making the world a little more secure HTB CAPE | OSEP | OSCP | CARTE | CRTO | CRTP
Joined May 2008
- Tweets1.6K
- Following511
- Followers847
- Likes4.2K



baas retweeted

Well, if any signature can reveal your private key, good luck getting any signed transaction on-chain without being frontrun and having your entire wallet drained before you can even perform your action and rotate your key.

Today I call upon the blockchain industry to calmly begin planning for "bunker mode". My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash.
Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase).
Don't rush. While I believe there is cause for action a rushed migration would do more harm than good. Don't panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets.
IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By "break" I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster).
Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture. In hindsight, May's unexpected disproof of the Erdős unit distance conjecture was our warning shot.
Yesterday's OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time?
Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.)
Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once.
Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I've witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case.
I urge large, sophisticated actors to lead by example. Project11's "risq list" (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I'll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026).
Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from "Satoshi's shield", i.e. his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS.
Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security.
The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I'll be pushing for maximum defensive acceleration.
baas retweeted

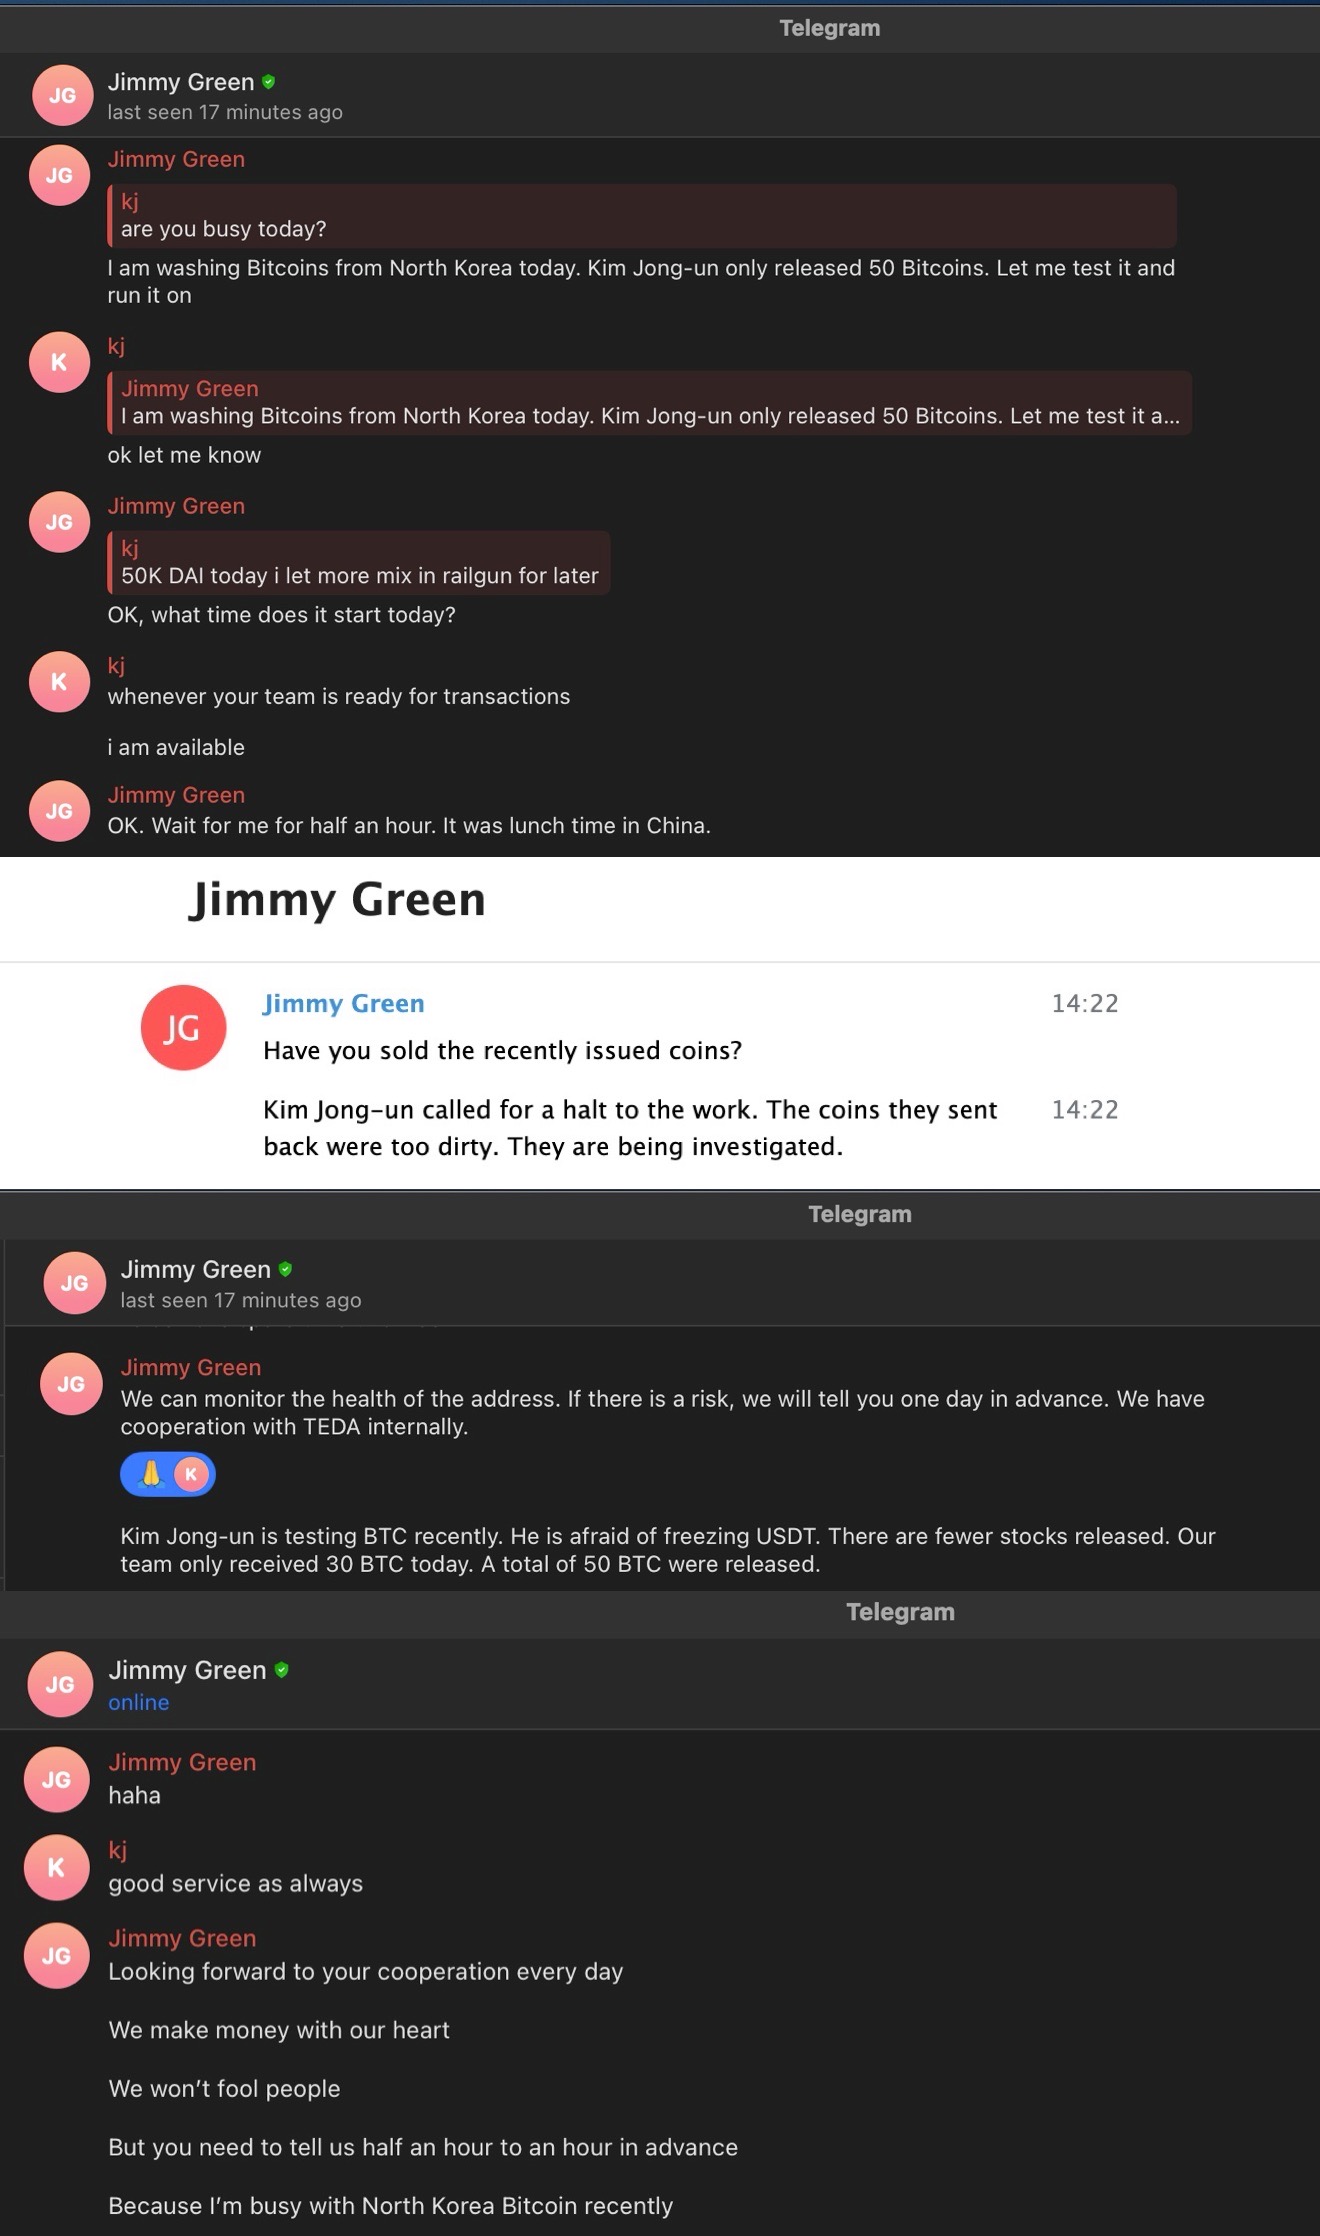
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.


baas retweeted

How I Could've Accessed 17 Trillion Microsoft Records
blog.faav.net/how-i-couldve-… :)

baas retweeted

🚨BREAKING: @Solana has flipped @RobinhoodApp to become the No. 1 chain for tokenized commodities spot DEX volume, with a 45% market share.
Just three weeks ago, Solana held only 1% of the market.


baas retweeted

AI made the most cracked people 1000x their capabilities, and turned the rest of the world into a literal bot network
baas retweeted

KYC = kill your customer

Did you get an email from @Revolut mentioning that your data has been leaked?
If so my condolences and ... well the trove of data in this case seems quite very bad.


baas retweeted

I resigned from Anthropic today. I spent the last three years doing pretraining research at both OpenAI and Anthropic. Neither company is acting responsibly. They are racing straight to self-improving superintelligence and gambling with our lives. More thoughts below.

baas retweeted
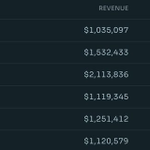
StonkFun Revenue
(Sept 7th)
Revenue: $1,198,987
Buybacks: $719,516
Burned: 5.67M solana:6GmAFSYs4gk3FDao5FzzySQpPZaWsa4rUJHacpMpUNgx
stonkfun.xyz/revenue


baas retweeted

FalconFlank : Crowdstrike Falcon 0day LPE is now public
github.com/MSNightmare/Falco…

baas retweeted

Red teamers gonna red team.
github.com/tailscale/tailcat

baas retweeted

o hacker do gta 6 montou simplesmente o pipeline de opsec mais absurdo q eu já vi
site em arweave, conta descartável no session e taxa de contato em $XMR onde as casas decimais são o ID unico pra abrir a conversa
o maluco buildou um protocolo inteiro de comunicação anônima só pra negociar vazamento, slc

O hacker do GTA 6 inventou o sistema de contato mais insano que já vi
Ele tá vazando toda a gameplay e está pedindo 400 monero:native (R$ 900 mil) só pra você conseguir falar com ele.
O site deles está hospedado de forma descentralizada em Arweave, lembra da arweave:native ?
Quando você clica na aba “Contact”, o site faz automaticamente:
- Cria uma conta nova e anônima no Session (um app de mensagem super privado, tipo um WhatsApp que ninguém consegue rastrear)
- Te entrega uma frase secreta de 12 palavras (é a senha da conta. Perdeu = perdeu pra sempre)
- Gera um valor único de Monero, tipo:
400.818811529987 XMR
Os números depois da vírgula são um código secreto único da sua conta.
Você precisa mandar exatamente esse valor de uma carteira pessoal (Cake Wallet, Feather etc.). Se mandar de exchange, arredonda e ele nunca te encontra.
Quando a transação aparece na blockchain da Monero, ele lê os números depois da vírgula, descobre sua conta Session e te chama.
Absurdo de sofisticado, essas blockchains de privacidade são bem ousadas e tenho incerteza quanto ao futuro.

baas retweeted

Want to run an entire Tailscale daemon from memory inside a C2 implant with zero disk artifacts, no kernel drivers, traffic indistinguishable from HTTPS to a CDN, and relay connections from the victim network back through the tailnet.
Now you can. Enjoy!
netspi.com/blog/technical-bl…
