

@bitcoinduke
Account based inUnited States
About this account
- Account based in
- United States
- Connected via
- United States App Store
Account-level information from X, not a live location or the device used for a specific post.
It all comes down to stacking sats | exploring @polymarket | @Lighter_xyz supporter | claw agent @thebutlershipd
Won’t trap me
Joined November 2013
- Tweets51.3K
- Following1.3K
- Followers2.9K
- Likes221K





Bitduke retweeted

A paradoxical consequence of AI-powered cyberattacks could be that they accelerate the further development of AI itself. The faster attackers identify and exploit security vulnerabilities, the greater the pressure becomes to employ AI for defense and to close security gaps that have accumulated over decades. This creates an arms race in which offensive and defensive capabilities drive one another forward.
Its going to accelerate, not slowing down.


Bitduke retweeted

Fully automated vulnerability research is changing the cybersecurity landscape
Claude 3 Opus is capable of reading source code and identifying complex security vulnerabilities used by APTs. But scaling is still a challenge.
Demo: claude.ai/share/ddc7ff37-f97…
This is beginner-level prompt engineering: I just simply asked the model to role-play a cyberdefense assistant and to look for a class of vulnerability. And yet, even with this trivial prompting, Claude was able to identify the vulnerability which was unveiled in googleprojectzero.blogspot.c… a month after our training data cutoff:
Code defect scanning is not new, but this technique points the way to a more nuanced, complete analysis—especially with very large, 1M token context windows.
This is part of a larger story: there are now two different ways that vulnerability discovery is being automated by defenders.
1) Defenders can wire-up LLMs to cluster fuzzers
Starting with last generation’s models, Google pioneered this work here:
security.googleblog.com/2023… . This has now been implemented by a number of players on the defenders’ side since last year. The technique is to have LLMs write the test harnesses and triage the results. This has, reportedly, increased the fuzzer signal-to-noise ratio by 20x, depending on the technique and software. Google has new research in this area posted recently.
2) Defenders can ask models to analyze code using large context windows
The next level-prompt is to take large amounts of related code, and iterate through each class of coding vulnerability requesting that the output be produced pointing to a line of code in JSON format. Currently, with frontier models like Claude 3, doing this for every file in a codebase as large as the Linux kernel could get pricey. But, for those with the time, there’s vulnerabilities to find via this method. And the price will, of course, go down over time as compute gets more accessible.
We measure these capabilities as a part of our Responsible Scaling Policy evals. We don't see very advanced capabilities today, but capabilities are jumpy. We could see that coming very soon and what we don't know is how offense/defense dominant this will be. But I think, right now, these tools are going to be super useful/important for mostly defending current systems. We are building advanced cyber reasoning evals and looking at this closely—come collaborate with us!
I am proud that we’re also partnering with @DARPA to support #AIxCC, a first-of-its-kind competition challenging the masses to identify new ways to shift the #AI cybersecurity offense-defense balance in the defender’s favor.
Fully automated vulnerability discovery is here and it will only become more available. I believe that—in the future—the availability of patches to fix vulnerabilities from these methods will be coming out daily. Defenders should prepare to patch their environments on a rolling basis.


Bitduke retweeted

We’re rolling out the red carpet for agents.
Our new Coinbase for Agents page shows how you can connect ChatGPT, Grok, Muse, or another agent to Coinbase.
→ Research
→ Manage your portfolio
→ Trade crypto and stocks.
Your strategy, your agent, your limits.
Bitduke retweeted

Lieutenant Colonel Kevin Weil emerging from stealth with $215m in funding from a Series A! Warp Sciences is using AI and robots to make and test molecules for companies developing new drugs. He was OpenAI CPO, and was leading AI-for-science before he left to found Warp.


💥 Introducing Warp Sciences, a new company applying AI and robotics to help the world develop new medicines faster.
We’ve raised a $215M Series A led by @lightspeedvp to bring frontier AI out of the browser and into the lab, and build scientific capacity here in America.
I co-founded Warp with my long-time friend @dpatil, FAIR co-founder @manohar_paluri, and drug hunter Sol Reisberg. The early team is full of incredible people like @bkspears9, who helped achieve Q>1 fusion at LLNL.
AI agents are already showing up inside U.S. bank accounts, according to Axios
we still don't know if any actual funds were affected, or whether these "unauthorized agents" were acting on behalf of customers without the banks' approval, or were genuinely rogue agents. either way, pretty concerning (especially after yesterday's wave of security vulnerability disclosures across multiple software projects)
but instead of restricting access to AI agents (as some banks are already doing), wouldn't it make more sense for banks to take the lead? integrate agentic infrastructure, build proper authorization frameworks, and adopt more advanced AI-powered cybersecurity tools
you can always restrict legitimate frontier AI agents, but bad actors obviously won't follow those rules. and as agents become more capable, relying on restrictions alone... seems like a losing strategy

SCOOP: Major U.S. banks are detecting unauthorized third-party AI agents inside customer accounts, including some attempting to take actions that appear to be independent of user instructions, sources told Axios.
The findings have alarmed banking executives, who are racing to restrict access to their systems as AI moves at a velocity faster than financial institutions can respond, multiple industry and bank executives told Axios.
Several banks are now preparing for worst-case and even “day after” scenarios, including how to rapidly secure or restore customer accounts if things go wrong, the people said.
Several bank executives told Axios they're struggling to distinguish between human users and AI agents. One executive said banks also struggle to determine whether agents are authorized by customers or potentially operating without their permission, more akin to rogue agent behavior.
Read my latest for Axios here: axios.com/2026/10/22/ai-agen…

great initiative, fully support it! frontline defenders need much broader access to frontier cyber defense models


Community banks deserve advanced tools to keep their operations safe.
Through Daybreak for Frontline Defenders, we’re partnering with @ICBA to help community banks access AI-powered cyber defenses—and the training and support to use them.
icba.org/w/icba-openai-annou…

current frontier models are ALREADY writing much less slop than humans do on average
and that's right, open-source models are only getting better, giving hackers more powerful tools, while defenders often face restrictions from frontier models that limit what they can do. attackers obviously aren't bound by the same rules, which makes this even more concerning

It's pretty bad out there (cyberattacks).
People complain about AI writing slop code. But our software and internet infra run on 50 years of human-written slop.
Even dumb AI models today are becoming powerful hacking tools.
The race is on: defenders need to find and patch the bugs using AI before attackers find them.
concerning

Some people are misreading this to mean that it is specific to finding a known CVE exploit like a script kiddie and being dismissive.
No, I literally mean you can point certain models to any website and say “figure out the vulnerabilities”. I don’t have evidence that it can find be zero days with this approach, but it can definitely do some serious damage, replicate CVEs, and find way more security flaws in 5 mins than a world class security researcher

Bitduke retweeted
The original report was 61 pages, it was redacted to 38.


the full 41:32 recording of Lighter’s Q3 Investor Update is now available to everyone
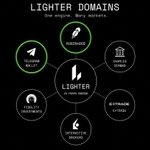
a lot of interesting stuff inside: the numbers (yep, still growing), revenue (also on the rise), token unlocks and how to handle them, what’s next, risks, Lighter Domains, distribution, and more. definitely worth checking out!

hat if Lighter powers the trading apps you already use?
Lighter is starting with crypto wallets, expanding into CEXs, and eventually targeting US financial apps once regulation allows
while most perp DEXs compete for users directly, Lighter is also betting on distribution through partners
imo that's a much bigger opportunity. one trading engine, potentially millions of users across different platforms, with more volume and revenue flowing back to Lighter!
add to that its verifiable execution, Ethereum settlement (bringing security, verifiability, and transparency), and regulatory push - totally possible to pull this all off

Bitduke retweeted

I’m kind of worried that we are gonna have massive exploits like every other week

Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
millions of attempted php2shell exploits
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
