

MAKING THE INACCESSIBLE, CESSIBLE. The views expressed are all my own, and do not represent my employer....
Joined March 2009
- Tweets29.1K
- Following5.1K
- Followers4.1K
- Likes57.4K




Pinned Tweet
So put down that burner phone at @Target an pick up some chonies to drop in @drkR4bbit bin...do some good instead of perpetrating FUD
John Stauffacher retweeted

The U.S. has a trillion dollar defense budget
It also has dudes like this, just in case
Writer: Michael
Kinda bummed they didn't finish the set last night with this...though the 2000+ people marching to the parking lot made up for it...most interesting venue exit I've been a part of in a long time.
Awesome show though, 18,000+ singing along to every song..
open.spotify.com/track/5dTHt…

John Stauffacher retweeted

Upcoming Incident Analysis Trainings (Basic & Advanced) by @ERNW_ITSec
hm-ts.de/seminare/courses/in…

John Stauffacher retweeted

Several people have requested an update on the Black Hawk helicopter that landed in a Las Vegas neighborhood earlier this week.
It’s not going well.

John Stauffacher retweeted

I appreciate that L.A has pure madness for options tonight
My Chemical Romance, Weezer & SSPU, Gorillaz, Jay Z, Marshmello, Animal Collective, The Offspring, Madeon, Gryffi, Kool And The Gang & Zapp Band
endless choices that doesn't even include the small venues.
Have Fun!


John Stauffacher retweeted

We’re still testing how exploitable the Node.js/Brotli bug is, but we’ve found that it’s surprisingly hard to tell whether you’re even affected.
So @ToBScottA built a scanner that finds hidden copies of the decoder, even in stripped binaries.
github.com/trailofbits/brotl…

John Stauffacher retweeted

I'm a Security Engineer at AWS. I started as an Incident Responder with CIRT, moved to managing my own team, and now I manage the AWS Security Communication team
Ask me anything :)
(I hold the right to refuse to answer questions that could get me fired.. also, 2 hour limit).

John Stauffacher retweeted

This is absolutely f*cking insane.
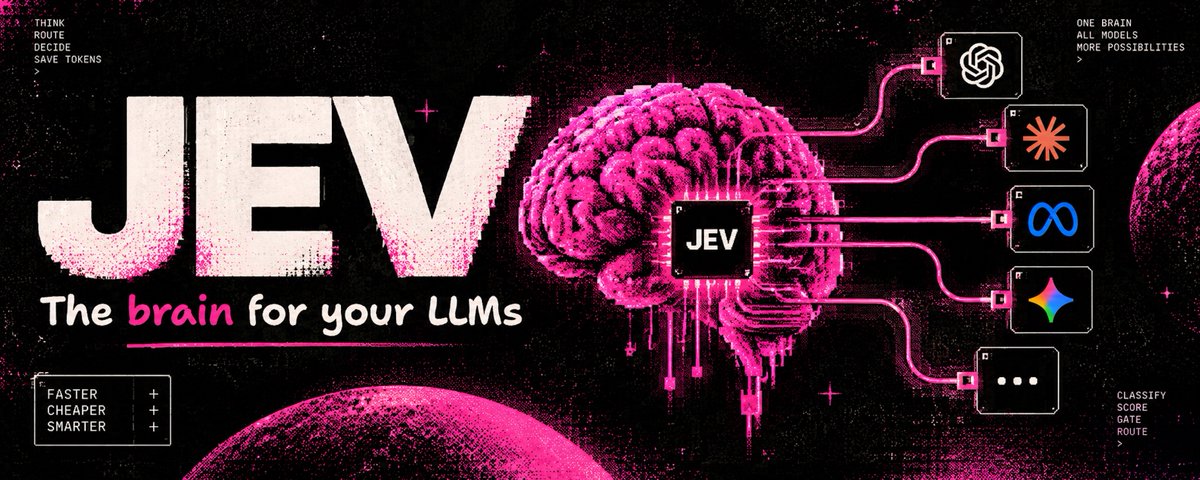
you can put a $0.042-per-million-token model in front of Claude and let it decide what Claude ever has to see.
that's Jev signal routing, and the trick is stupidly simple:
Jev takes the first look at everything. Claude only gets the hard cases.
instead of:
data -> Claude -> tokens burnt $
it's:
data -> Jev -> only the unsure ones -> Claude
and here's the part people miss. every Jev answer comes with a probability. that's your router:
-> Jev is sure? its answer is final
-> Jev hesitates? the case goes up to Claude
set the cutoff once, by testing on your own data, not by guessing.
3 repos that already do the routing for you:
-> duckdb-jev: route your data. Jev labels every row straight from SQL, up to 1,000 calls in one request
github.com/prasanthj/duckdb-…
-> quicksilver: route your files. Jev checks all 187 files in parallel and Claude gets the 4 that matter. ~2.4k tokens instead of ~26k
github.com/UditAkhourii/quic…
-> jev-router: route your models. before every message Jev decides simple or hard and sends it to the fast model or the strong one. works with your normal Claude login
github.com/gargpratyush/jev-…
where this pays off right away:
-> support tickets
-> your inbox
-> lead lists
-> messy spreadsheets
-> comment moderation
on a public benchmark Jev labeled 1,000 rows for $0.015. Claude charged $0.80 for the same job.
faster. cheaper. way fewer tokens burned.
Jev sorts the mail so the genius only opens what matters.
Claude thinks. Jev routes. code does the job.

John Stauffacher retweeted

mw00/project-maya: Project Maya - run GLM-5.3-Flash (321B MoE) and DeepSeek-V4.1-Flash-1017 (748B MoE) privately on your own GPU(s), from one card to 16, NVIDIA or AMD, Linux or Windows. Engine, server, dashboard, OpenAI- and A... github.com/mw00/project-maya

John Stauffacher retweeted

THIS IS ACTUAL F*CKING GOLD
Anthropic just shared one of the best tricks for Claude Code.
The idea: stop configuring Claude Code by hand. One prompt, 44 seconds, and your whole .claude/ folder writes itself.
7 files, 162 lines, 2 cents. you typed one line and wrote zero of them.
You just launch Claude Code like this:
claude --model opus "set up this repo: ..."
here's the split:
→ 3 Haiku 5.5 agents scan the repo before a single file gets written
→ one reads the stack, one reads the npm scripts, one hunts for risky paths
→ Opus 5.5 takes those three summaries and writes the actual config
→ 7 files land: CLAUDE.md, 3 agents, permissions, a format hook and a /ship skill
the part everyone gets wrong: they write CLAUDE.md from memory.
a config written without reading the repo is a guess, and you live with that guess for months.
here the risk scan came back with 5 dangerous paths and those went straight into the permissions file, so the agent is blocked from them before it ever runs once.
the scripts scan found 5 npm scripts, and the agents got wired to the ones that actually exist in this repo instead of generic placeholders.
one prompt from you, 7 files from it, 0 lines written by hand.
Haiku reads. Opus writes. You commit.
JEV engineering is the same move one layer down: 1,867 forks this run - which file, which agent, allow or ask - resolved in code at 0.97 sharpness, and the split ones (0.59 on "allow or ask") come back to you instead of being guessed
the full tree
▸ you paste one prompt describing the setup you want
▸ 3 Haiku 5.5 agents scan stack, scripts and risky paths in parallel
▸ every agent returns a summary, never raw files
▸ Opus 5.5 writes CLAUDE.md, the agents, permissions, the hook and the skill
▸ anything touching permissions comes back to you before it is written
▸ JEV resolves micro-forks in code and escalates only the split ones
paste the tree and this prompt into Claude Code ↓
"Set up this repo for me:
1. First scan it with 3 Haiku 5.5 agents in parallel: one reads the stack and manifests, one reads the build and npm scripts, one finds paths that are dangerous to touch.
2. Each agent returns a summary only, never raw file contents.
3. Then write CLAUDE.md, 3 subagents, a permissions file, a format hook and a /ship skill, all based on what the scan actually found, not on defaults.
4. Every risky path from the scan goes into the deny list before anything runs.
5. Ask me before writing anything that grants permissions.
Show me every file as a diff first. No writes until I say go."
↳
code.claude.com/docs/en/mode…
save it, this is the first thing you run in every new repo.


John Stauffacher retweeted
Every Mac on macOS 27 now has a free LLM built into the Terminal.
No account. No API key. No internet. No token bill.
Setup (1 minute):
1. sudo fm license (enter your Mac password, one time)
2. fm available (checks the model is downloaded)
3. fm respond “your question”
Works on any Apple Silicon Mac, M1 included.
- Pipe files: cat notes.txt | fm respond -i “summarize this”
- Get JSON back: build a schema with fm schema object, pass it with --schema
- Local API: fm serve gives you an OpenAI-compatible endpoint on localhost
- Resume chats: sessions save to ~/.fm/sessions/
The limit is 4,096 tokens per session, and your prompt, instructions, and the answer all share it.
So skip code and math. Use it for summarizing, extracting, classifying, and rewriting.
Free, private, offline, and already on your Mac.

John Stauffacher retweeted

Update: Our PHP exploit is now production-grade.
* stock php.ini-production, display_errors=off, normal memory_limit, multi-worker, ASLR, under load
* ARM64 + x86-64 targets
* MediaWiki, WordPress, phpBB, Laravel
* Apache/mod_php and nginx/php-fpm -> root
xitter.cf/dguido/status/21131291…

Re: the widely circulated blog claiming the PHP bugs aren't easily exploitable: @trailofbits has a working exploit that gets a shell on an unmodified MediaWiki installation.
eliastaylor.com/noexploit/

John Stauffacher retweeted

Many teams SUCK at making software, and “patch everything” is so short-sighted.
Vulnerabilities are a symptom of a larger problem. We’ve been getting away with a lack of engineering rigor for a long time (decades) in most industries.
We’re not making resilient software. We will continue to have issues until most orgs mature how they build, no matter how many times a day you patch.
It’s been a financial decision to prioritize shipping fast, over minimizing brittleness.
As exploitability gets cheaper, it drives up response and maintenance costs.
This may finally incentivize orgs to invest more in software resilience.
And we have the tools: each dev team can now spend tokens analyzing their own code and deployment for security and availability issues. Automate testing, automate dependency upgrades, hold design review and threat modeling sessions.
Slop is what you make it if you’re not investing in mature architectural decisions. And we’ll keep having trivial vulns until you do so.

John Stauffacher retweeted

It took 17 minutes to turn the Gitlab RCE to a working HEAP exploit using Gemini 4 Argon and the advisory, then another hour for the complete chain - super fun for someone like me without any binary exp or source code review experience, new cyber era!
Great find by @joaxcar!


🚨 CRITICAL: GitLab flaw (CVSS 10.0) affects 12 years of releases.
CVE-2026-110264 could allow unauthenticated remote code execution on self-managed servers.
Read - thehackernews.com/2026/10/cr…

