

🥷 get protected with https://teapawt.net/t.co/jtZvIltVOx 🧑💻 local AI with https://teapawt.net/t.co/pQKDykIf77
building on →
Joined June 2007
- Tweets1.6K
- Following381
- Followers18.9K
- Likes2.4K




Hexabl0b retweeted

‼️ EU governments approved a GDPR change to let companies train AI on Europeans' personal data without consent.
It makes AI training a possible "legitimate interest", judged case by case. Parliament must still agree.
Max Schrems calls it a "digital expropriation" of Europeans.


Hexabl0b retweeted

Per-event API lookups and DNS volumes don't mix. The rate limit shows up long before the answer does. 🐢
So we're teaming up with isMalicious, the Paris-based threat intel provider that publishes domain and IP indicators as STIX over TAXII. Tenzir keeps them in a local lookup table as #OCSF and tags matching DNS and network events while they're still in the stream. Each match carries its sources, risk score, and validity dates, and nothing calls an API per event.
Open standards in, open schema out. Our blog post shows how the pieces fit and where to start.
tenzir.com/blog/threat-intel…

Hexabl0b retweeted
I highly recommend cloudflare's security audit skill: github.com/cloudflare/securi…
Run it on all your software. Run it with the free models. Use it even if you used a model to audit something - it will find much more things. Works in all agent harnesses and is model independent.

Hexabl0b retweeted

Always have a comma in your password, if part of a leak it will break the CSV.
Follow me for more cybersecurity advice.
Hexabl0b retweeted

Effect v4 is here.
One ecosystem. Zero dependencies.
The next chapter of Effect and the foundation for building reliable software and AI agents in TypeScript.

ALT Effect 4.0 stable release announcement on a dark background. Large white “4.0” above “Production-ready. Out now.” A timeline along the bottom progresses from 3.0 Stable to 4.0 RC to 4.0 Stable.
Hexabl0b retweeted

We started Codex for OSS six months ago.
Today, we’re renewing the program with $100 Pro plans and doubling the number of grants (from 5,000 to 10,000) to reach more maintainers.
(If you received a grant previously, we encourage you to re-apply!)
openai.com/form/codex-for-os…

Hexabl0b retweeted

"Propagate user authorization context in AI agents with Amazon Bedrock AgentCore".
aws.amazon.com/de/blogs/secu…


Hexabl0b retweeted

FastMCP 4 is finally GA.
Built for the MCP 2026-07-28 rewrite: requests are sessionless, any replica behind a normal load balancer can answer, and the client negotiates old vs new protocol per connection so sticky sessions can finally retire.
You also get interactive tools that pause for approval, background tasks via fastmcp-tasks, ClientGroup for multi-server agents, cache hints, and gateway routing headers. Most FastMCP 3 apps upgrade without code changes.
Sticky session stores were the tax we all pretended was fine. Stateless MCP is the adult version.
github.com/PrefectHQ/fastmcp…
Hexabl0b retweeted

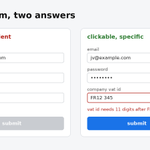
most submenus close on you when you aim at the bottom of one.
your cursor cuts across diagonally, clips the row underneath on the way, and the menu reads that as you pointing at something else. so it shuts. you've probably trained yourself to go sideways first and then down, without ever noticing you did.
the fix is a triangle. while your cursor sits between the point it left the row and the submenu's near edge, the rows it crosses stop counting. amazon has shipped this for over a decade.
ben kamens took it apart in 2013, and it's usually called a safe triangle. i put two menus side by side in the post. same rows, same submenu, one of them has it. try to reach trash in both and see which one lets you.
full read link in comments ↓ it's interactive :)

Hexabl0b retweeted

LoopArena
Benchmarking Models as Runtime Controllers for Loop Engineering
paper: huggingface.co/papers/2608.2…
Hexabl0b retweeted

An introduction to technical AI safety research: alignment, reward hacking, robustness, agents and more, before we turn these ideas into data, Python and reproducible experiments.

Hexabl0b retweeted

From prompt injection to supply chain attacks, learn how to actually break AI systems.
Attacking AI Systems: Threat Model to Exploit
📅Sep 3 | 3:00 PM - 8:00 PM GMT+2 | On Zoom
Two hands-on group practicals. Real architecture. Real attacks.
✅Save your seat: luma.com/pfpgt4mw?utm_source…
Hexabl0b retweeted

I love experimenting with architecture and light, so I recreated the Louvre Abu Dhabi in code, including its signature Rain of Light. Camera exploration spans the waterfront, the museum city, and views from beneath the lattice.
Code → Kimi K3 + Devin AI + Three.js
Hexabl0b retweeted

Anatomy of Microduck 🤏🦆 :
* 15 robotis dyanmixel XL330-family servos
* rockchip RK3566 compute
* np-f550 battery
* camera, 8×8 ToF LiDAR + dual IMUs
mishig-microduck-anatomy.hf.…
Hexabl0b retweeted

Added physically-based Location + Date Time aware sun positioning to @mrdoob's new #ThreeJS sunlight. Much easier to simulate day/night cycles than trying to figure out how to move the sun via manual azimuth/elevation modification.
github.com/mrdoob/three.js/p…
Hexabl0b retweeted

I've built a new opensource Third-Person Soldier Stage in the browser, built with @threejs.
4 techniques, 4 abilities, 2 boons, endless procedural night terrain, ragdoll deaths with no physics engine, katana & gun play.
All GLSL. No engine, no physics lib, no asset pipeline. This VFX showcase is an extension of my previous projects to showcase customizable VFX that can be a easily implemented in your projects.
Source code: github.com/achrefelouafi/Sol…
Live link:
soldierthirdpersonthreejs.pa…
Hexabl0b retweeted

When an aircraft goes down, wreckage is preserved by law and the investigators have subpoena power.
However, when AI goes rogue, the investigations are at the pleasure of the company being investigated.
I have unanswered questions.
My latest: blog.peterwildeford.com/p/ro…
