

An @Intell_on_Chain service | Report in Telegram - https://xitter.cf/t.co/Qlwzd84Bjk or use the website below
Get started 👉
Joined March 2023
- Tweets18
- Following290
- Followers392
- Likes559

Pinned Tweet
Why should someone who's already lost everything have to pay just to find out what happened?
It's a question we asked ourselves.
And it's why @Intell_on_Chain launched IOC Support.
A completely FREE initial assessment service for victims of cryptocurrency fraud and theft.

Potentially $2M in fraud identified
The scammers approach victims on @indeed initially
They targeted people looking for work to entice them to join an investment platform.
Heres more info:

Our website has had an upgrade!
It’s now very easy to open a case! Anyone who has lost assets to crypto-related fraud is welcome to grab help!

We use our blockchain investigation experience to help victims understand what happened, where their funds may have gone and what options they have next.
Sometimes those options are limited. Sometimes there are investigative leads worth pursuing.
IOC Support retweeted

I'm putting these patterns out there in the public domain! If they're of interest please get in touch!
💵 13,000 ETH @ ~$3,021.76 per ETH
💵 Total - $39.3M at the time of withdrawal!
✍🏼 There are two identical patterns - Almost exactly the same! One was 6K ETH and the other 7K ETH 😱
Get tagging folks 🕵🏼♂️
🍥 Withdraws from Tornado's 100 ETH Contract April Last year
⬇️⬆️ Swaps for WETH
🌉 Bridges to Avalanche (WETH.e)
⚞ collate in a buffer wallet and remains even now, more than 18 months later.
The balances do not show on @SnowTraceHQ or @DeBankDeFi but do on Arkham - Really intriguing. Could be cross chain transfers to other @avax chains
Here is the other pattern, which was a week or two before the above example!
If you're missing $39.3M, please DM!


IOC Support retweeted
Last night the whole community came together and prevented people from having all of their crypto stolen!!
Scam websites and Discord. (Do NOT navigate to these links)
⚠️//Dragonary.org @Namecheap This is a request to take down their website please
⚠️//discord.gg/dragonaryland @discord
This is the story & how to spot these scams for yourself! ⬇️
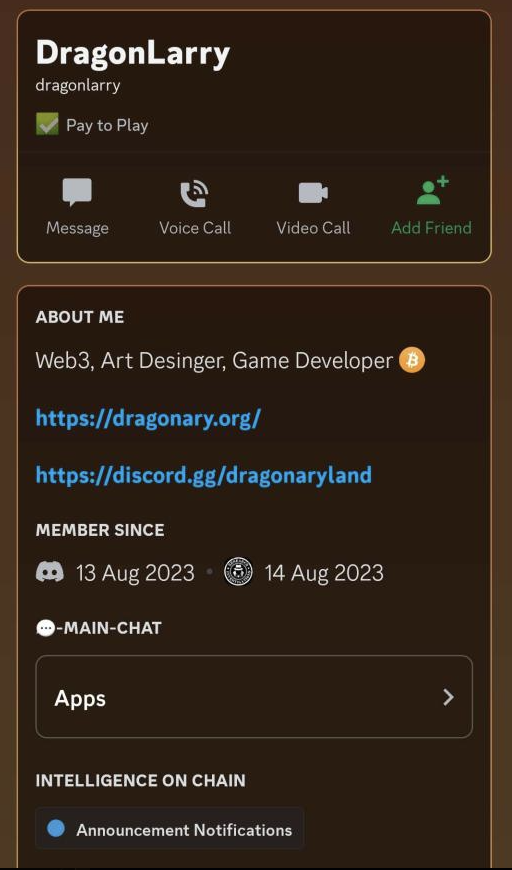
It starts of pretty innocently. DragonLarry (Discord ID:1140300424985972817) comes in and greets us with a sticker!
This was where the first red flag came from! A quick look at his profile, reveals that the account is a day old 🚩
This alone is not enough to be suspicious... It's just odd.
So, I say to my guys to keep an eye on the profile...
Low and behold, one day later, the potential attack begins... It's fair to say, at this point we're not 100% sure but we'll play along with it!
⚠️ Our community awakens 😅
The first thing is first, I warn the community!⚠️ The last thing I want or need, is for someone to become a victim in my own server. We did say to the potential scammer (later we confirm this) that we'll publicly apologise if we have this wrong.
I've written about these types of alluring techniques used by such scammers up on the website! You can find more information here: intelligenceonchain.com/mali…
Anyway, we set about testing the contents of the supposed game! We have @OxSaiyanGod @_cyberunicorn @WoAS_Necksus and to thank for scoping it out. There were virtual machines firing up all over the place but a quick scan of Virus Total revealed a lot of information to us!
So, it wasn't too long before we were able to confirm that Larry was indeed a scammer, trying to steal money from our community members. Luckily, we have a safety conscious community who could see this a mile away!
Be careful though, the tactics they use are very convincing. If you want to see the events that unfolded in real time, head to Discord and you can find the conversations from this moment: discord.com/channels/9458317…
Stay Safe
A direct quote from Larry:
"so.. the acquaintance didn't go as planned"
Further credits to @Thealphacruze @noohp_ @HumbleBumble_O @Frizmond @JPOnChain @CryptoSunriseX @pingToven
@Cipher0091 For being alert, suspicious and for helping!! We have an awesome community!


IOC Support retweeted

The phishing contracts used by Inferno Drainer have recently undergone an upgrade. These phishing contracts now possess the ability to steal users' ETH, ERC20 tokens, and NFTs.
Let's consider phishing contract 0x000056 as an example. The claim function is specifically designed to pilfer users' ETH, which is then transferred to a central hub contract with the address 0x0000da. This hub contract serves as a collection point for stolen ETH from various phishing contracts. Consequently, a phisher such as 0x000055 (Fake_Phishing182232) can invoke the withdraw function of the hub contract to facilitate the transfer of the stolen funds.
Simultaneously, the multicall function of the phishing contract is employed to transfer users' approved ERC20 tokens and NFTs, incorporating a built-in profit-sharing mechanism.
We have promptly reported all associated contracts to Etherscan. Please exercise caution and remain vigilant.
Check the fund flow:
metasleuth.io/result/eth/0x5…
metasleuth.io/result/eth/0xc…
metasleuth.io/result/eth/0xa…


