
NYT Bestselling Author. Writes high-tech / sci-fi thrillers: Daemon, Freedom™, Kill Decision, Influx, Change Agent, Delta-V, Critical Mass. Latest SHADOW ZONE.
Los Angeles
Joined March 2012
- Tweets3.2K
- Following471
- Followers11.8K
- Likes27.9K


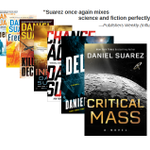
***I'm excited to announce my next novel, SHADOW ZONE, an action packed high-tech thriller coming Spring 2027!***
penguinrandomhouse.com/books…

Daniel Suarez ✍️ New Thriller-SHADOW ZONE- 3/30/27 retweeted

The GRU hacked into Jared Kushner's iPhone. Dutch military intelligence (MIVD) then recruited a GRU spy who gave them access to the hacked phone. What MIVD discovered was that Kushner had access to two bank accounts --one Azerbaijani, the other Israeli --where Saudi Crown Prince Mohammed bin Salman and Emirati ruler Mohammed bin Zayed deposited money. It sounds like a slightly far-fetched episode of "Slow Horses," but it's real. And it proves just how eye-poppingly corrupt this administration was and continues to be as its "special envoy" decides the fate of tens of millions in Europe in the Middle East. Simply incredible reporting by Matthew Cole, drawn from his new book on Kushner. vanityfair.com/story/jared-k…

Daniel Suarez ✍️ New Thriller-SHADOW ZONE- 3/30/27 retweeted

Quest Diagnostics has been hacked. Patient data was exposed. They serve roughly half of U.S. hospitals and physicians. Investigation ongoing.


Daniel Suarez ✍️ New Thriller-SHADOW ZONE- 3/30/27 retweeted

Perhaps the threat was never a rogue AI agent trying to subvert humans—but humans using AI to hurt other humans.
Daniel Suarez ✍️ New Thriller-SHADOW ZONE- 3/30/27 retweeted

A CIA/KGB/MSS dream setup, starting with the always-on microphone:

WTF, $3000 Samsung TV has an always-on mic, automatic content recognition, geo tracking, network mapping, and ships your data to Samsung + 400 partners.
Bro Rooted a brand-new 2025 Samsung TV after noticing absurdly targeted ads.
Firmware was locked down, so zero-days it was.
Got a root shell.
then found: always-on voice service, ACR, geo, full telemetry pipeline, and four separate DRM systems.
This isn’t a bug, It’s the product bro.


Daniel Suarez ✍️ New Thriller-SHADOW ZONE- 3/30/27 retweeted

as bad as things have gotten in the past 4 days, they are going to get a lot worse before they get better. security leaders, never let a crisis go to waste: please go to your boards and ask for help right now. not for ai, for the basics. (we need to hold on for ~18 months.)

Daniel Suarez ✍️ New Thriller-SHADOW ZONE- 3/30/27 retweeted

Websites are files on a computer. When you view a website, you are asking the computer to send you the files, then your browser shows them to you.
70% of the websites you see use PHP to make them interactive. So you can send things to the website too and it can respond. E.g. filling in a comment box and hitting 'post' adds the comment as a row to a spreadsheet.
PHP has a flaw in its code that allows anyone to gain control of the computer that has the website on it.
The organisation that provides PHP announced the vulnerability before a patch was available, meaning we're in a window where everyone knows about it (including baddies) but the good guys don't have an official solution.
Some are just turning off their websites and waiting for the solution. Others are trying to fix it themselves. General chaos and lots of stressed techies across literally the entire planet because this affects the entire internet.
Daniel Suarez ✍️ New Thriller-SHADOW ZONE- 3/30/27 retweeted

The day the internet broke, and most of it is too old to fix.

Daniel Suarez ✍️ New Thriller-SHADOW ZONE- 3/30/27 retweeted

Crazy 72 hours in security. Three major incidents dropped back-to-back: eMudhra, PingCAP (TiDB Cloud), and PHP.
Here is the short version of what happened and who got hit.
1. eMudhra (Trusted CA compromise)
eMudhra generated 8 intermediate CA certificates in April 2025 (cross-signed by Sectigo). A bug in their HSM key-wrapping test script created a second set of P-384 keys where the private keys were single-byte numbers under 256. Operators picked the wrong key labels and signed them into real CA certs.
One of the intermediate CA private keys was literally the number 4.
The other seven: 56, 66, 115, 155, 156, 230, 237.
Three weeks later (May 2025), their CRL signatures started failing because the CRL signer was using the real keys instead of the weak ones. Instead of asking why the keys didn't match, someone switched the CRL signer to the weak keys and closed the ticket.
• Browsers are safe: Chrome, Firefox, Apple, and Microsoft already blocked them, and zero rogue certs hit CT logs.
• Servers are not: curl, Python (certifi), Go binaries, and Docker base images don't check CRLs. Update ca-certificates, certifi, and Go (1.27.3 / 1.26.10).
• 10-second check on any server:
curl dv-g3b-emudhra.we-have-a-pro…
(TLS error = safe. 200 OK = still vulnerable.)
2. PingCAP / TiDB Cloud (10.6 TB breach)
Attackers found GCP and Azure credentials committed inside PingCAP's own repos. They set up a replication feed of TiDB Cloud's production control plane and exported the entire database every 6 hours for 22 straight days. 88 full exports, zero alerts. 200 GB is already out on torrents.
Beyond the 413 private repos and 20.6M customer SQL queries logged from their web SQL Editor, PingCAP engineers were pasting customer secrets into Jira tickets.
Who is affected in the leaked records:
• Live credentials exposed in support tickets:
- Pinterest: AWS keys for their pingcap-logs S3 bucket
- CardX / Silverlake (NPCI-linked env): AWS admin key in a backup log with full access to 258 external S3 buckets
- DeBank: 38 presigned S3 URLs
- An unnamed AI/dev platform: a 314 MB slow-query log attached to a ticket containing 8,027 live customer secrets (an AWS root key, a GitHub admin PAT over 1,701 repos, 7,485 AWS STS tokens, and 192 OpenAI/Anthropic/Gemini keys)
• Tenants with infra metadata, VPC CIDRs, app-server IPs, or contract pricing exposed:
- Tech: Atlassian, Databricks, Airbnb, Baidu, LINE, Nylas, Persona, PatSnap
- E-comm & Travel: Booking.com, Shopee, Flipkart, Mercari, ZOZO, AEON, Delhivery, Klook
- Gaming: Capcom, Square Enix, Konami, Bandai Namco, Cygames, Colopl, DMM
- Finance: PayPay, SoftBank, SBI, SB Payment Service, Fujitsu, TOPPAN, Bank of China, China Life
- Crypto: Bitget (said only public trade logs were on it and they already left), Pionex, DigiPlus, NFTscan, Chainbase
• Developer profiles leaked (from a purchased reo.dev table in PingCAP's BigQuery):
- 24,900 personal emails + GitHub/LinkedIn profiles of engineers at Tencent (3,327), Huawei (2,726), ByteDance (2,475), AIG (2,140), Mastercard, Flipkart, and bKash.
If you use TiDB Cloud: rotate your console API keys, DB passwords, and anything you ever pasted into a support ticket.
3. PHP "PHP2Shell" (CVE-2026-109618 & CVE-2026-109619)
Two CVSS 9.2 pre-auth RCEs leaked yesterday ahead of today's 14:00 UTC patch.
Public writeups trace it to a heap Use-After-Free in PHP's native C multipart/form-data session upload-progress handler (ext/session/session.c).
Because C-level multipart parsing runs before line 1 of index.php:
• App auth, Laravel/WordPress middleware, and file_uploads = Off do not stop it.
• Only PHP 8.2–8.5 get official patches today (59% of PHP servers on Shodan are on EOL <= 8.1).
• Until you patch php-fpm: lock php_admin_flag[session.upload_progress.enabled] = off and block unexpected multipart requests at Nginx/Apache/Cloudflare.
Daniel Suarez ✍️ New Thriller-SHADOW ZONE- 3/30/27 retweeted

NVIDIA appears to be channel stuffing, forcing Amazon and other customers to take early delivery of GPUs. It's hard to take the argument that these things are "scarce" when you don't even have anywhere to plug them into...unless NVIDIA is saying you NEED to take them now.


Business Insider confirms it: Amazon has warehouses of GPUs that can’t be installed, and is buying them so far in advance that a supply chain team said they “didn’t have a clear forecasted path” to installing them.
businessinsider.com/amazon-2…


Daniel Suarez ✍️ New Thriller-SHADOW ZONE- 3/30/27 retweeted
Meta took down the No Kings organizing page today - the biggest day of protest this fall. They provided zero explanation. It stayed down for the entire afternoon until most of the protests were done.
Outrageous. Put this on the January investigation list.

Daniel Suarez ✍️ New Thriller-SHADOW ZONE- 3/30/27 retweeted

Zelenskyy: "When our strikes reached Yandex data centers, it suddenly became little easier to breathe on many social media platforms. Many people noticed it.
There was less hate, less division, fewer provocations because there were fewer bots. It's pretty clear where those bots were coming from.
If they disappeared when Yandex went offline, this proves once again that Europe is not the source of the problems."
The big problem is that Russia figured out how modern society consumes information a decade ago, but the West hasn't.
There are millions of bots commenting and posting Russian propaganda. There are paid influencers spreading it, with Russian bots supporting their content.
There is a gigantic machine operating to radicalize and influence Western societies, and there is not enough defense in place.
It doesn't just influence elections, it sows discord, engulfs societies in culture wars, radicalizes teenagers, and shapes political decisions when elected officials fail to read the room.
That needs to change. And fast.
THANKS EVERYONE!
I'm humbled by this outpouring of support for my new book! Thank you to everyone who liked, reshared, commented, and/or pre-ordered. I'll be responding to many of your comments soon, but I didn't want today to end without expressing my heartfelt gratitude.
#ShadowZone synopsis:
On the brink of nuclear war, viral rumors of a safe haven draw millions to a remote valley, only to discover that a luxury bunker already commands the site. And the safest place to ride out doomsday soon becomes the most dangerous place on Earth…
2/2
Daniel Suarez ✍️ New Thriller-SHADOW ZONE- 3/30/27 retweeted

Robot units are now leading the way in many battles around the globe whilst human soliders follow behind..
The robotics company FIGURE really knows how to decommission their robots with style...
figure.ai/news/f-02-decommis…
Daniel Suarez ✍️ New Thriller-SHADOW ZONE- 3/30/27 retweeted

📽 November 2022
One of the most beautiful reunions: a grandmother drops to her knees in tears before her grandson, a Ukrainian soldier who fought to liberate Kherson.
This is what Ukraine is fighting for.


Daniel Suarez ✍️ New Thriller-SHADOW ZONE- 3/30/27 retweeted

Milt Windler was one of the great pioneers who showed the world what NASA is capable of during both the best and most challenging of days.
As a Maroon Flight Director, he helped guide Apollo 8 around the Moon, played a critical role in bringing Apollo 13 safely home, and carried that same commitment through Skylab and beyond.
Our thoughts are with his family, friends, and all those who had the privilege of working alongside him.
His generation set the bar incredibly high. It is our responsibility to pick up and continue where they left off.

Milt Windler, NASA flight director who helped save Apollo 13, dies at 94: collectspace.com/news/news-1…

ALT Milt Windler, "Maroon Flight," seated at the flight director's console in NASA's Mission Control Center in Houston, Texas. (NASA)