

Tech & cybersecurity journalist @InfosecurityMag Also behind @coupecircuit_ 🇫🇷🇬🇧
London, United Kingdom
Joined October 2011
- Tweets5.8K
- Following2K
- Followers1.6K
- Likes6K



Kevin Poireault retweeted

Sorry folks, we have a confirmed PHP compromise with post-exploit activity. Still not the widespread outbreak we all braced for, but it’s actively exploited in the wild. Updated threat brief:
unit42.paloaltonetworks.com/…

Kevin Poireault retweeted

Ah bah voilà, c'est parfait ça pour un vendredi !!
Allez hop, on remet ça.

‼️ BREAKING ‼️ PHP warns of another UNPATCHED REC vulnerability just 2 days after releasing emergency patches for critical PHP2Shell flaws.
New "CVE-2026-115560" affects only unusual session configurations. PHP has issued urgent mitigation guidance.
Full details → thehackernews.com/2026/10/ur…

Kevin Poireault retweeted

Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.”
A significant blast radius.
This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression.
Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.

Kevin Poireault retweeted

Une troisième faille critique dans PHP : la CVE-2026-115560
Pour s'en protéger en attendant la mise à jour :
"Set session.upload_progress.enabled=0 and restart every worker until the next regular bugfix release, to fully protect from CVE-2026-115560."
👉 cert.europa.eu/publications/…

ALT Affected Products PHP 8.5 versions prior to 8.5.12 PHP 8.4 versions prior to 8.4.27 PHP 8.3 versions prior to 8.3.36 PHP 8.2 versions prior to 8.2.35 End-of-life branches (PHP 8.1 and older), which no longer receive updates from the PHP project [4]
Kevin Poireault retweeted

PHP2Shell chaos, round three: Another PHP remote code execution flaw has surfaced.
More here: theregister.com/security/202…
theregister.com/security/202…

Kevin Poireault retweeted

A brief update on the critical vulnerabilities in PHP:
We have not yet validated exploitation in the wild and we have no evidence of successful wide scale exploitation. There are currently several exploit PoCs publicly circulating, many of which appear to be "vibe-coded" and are incapable of remote code execution. We have validated some PoCs, however, that are capable of RCE against default deployments of mod_php but not PHP-FPM.
Nonetheless, exploitation may have already begun in a limited fashion and the threat is viable and very serious. Defenders should:
1) Patch & Restart by upgrading to PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35 and restarting web services
2) Layer Temporary Safeguards at the network edge (WAF/proxy rules) and server configuration level if immediate patching requires a maintenance window
3) Protect Credentials by monitoring for abnormal session traffic and rotating keys and passwords on compromised internet-facing PHP systems exposed prior to patching
🔗 We are continually updating our Cloud Security blog post on this topic with real-world guidance and actionable defense strategies as we learn more. Please keep monitoring these posts for updates as you prioritize your patching efforts: cloud.google.com/blog/produc…
🔗 Technical details from Wiz: wiz.io/blog/php2shell-php-rc…
🔗 Details of the exposure from VirusTotal: blog.virustotal.com/2026/10/…

Kevin Poireault retweeted

Why php2shell can't be widely exploited
What limit the php2shell exploitation in practice
berardinellidaniele.com/post…

Kevin Poireault retweeted

SCOOP: Major U.S. banks are detecting unauthorized third-party AI agents inside customer accounts, including some attempting to take actions that appear to be independent of user instructions, sources told Axios.
The findings have alarmed banking executives, who are racing to restrict access to their systems as AI moves at a velocity faster than financial institutions can respond, multiple industry and bank executives told Axios.
Several banks are now preparing for worst-case and even “day after” scenarios, including how to rapidly secure or restore customer accounts if things go wrong, the people said.
Several bank executives told Axios they're struggling to distinguish between human users and AI agents. One executive said banks also struggle to determine whether agents are authorized by customers or potentially operating without their permission, more akin to rogue agent behavior.
Read my latest for Axios here: axios.com/2026/10/22/ai-agen…

Kevin Poireault retweeted

Security called me at 6:12 AM today.
"Patch every PHP server immediately."
I asked what happened.
"Two critical vulnerabilities. Remote code execution. No authentication required."
Cool.
How many PHP servers do we have?
According to inventory: 12
According to reality:
Nobody knows.
We found one running WordPress.
Three running old internal tools.
One under someone's desk.
Two inside vendor appliances.
A forgotten employee directory from 2016.
And a server named:
PHP-OLD-DO-NOT-TOUCH
Naturally, that one runs payroll exports.
Then we found a PHP 5.6 box.
I asked who owned it.
The documentation said:
BRIAN.
Brian left in 2019.
We called Brian.
He said:
"Oh wow, that's still running?"
Excellent.
By 8 AM, leadership joined the incident call.
CEO:
"Can hackers actually get in?"
Security:
"Potentially yes."
CEO:
"Without a password?"
Security:
"Yes."
CEO:
"Then why do WE need passwords?"
Not the lesson.
Finance asked if we could wait until the weekend to patch because downtime affects revenue.
Security explained that the alternative was letting strangers execute code on our servers.
Finance asked for a cost comparison.
At 9:17, someone suggested temporarily taking the vulnerable websites offline.
Marketing refused.
"Our campaign is live."
So for the next hour, the company officially decided maintaining a landing page for 20% off webinar registration was more important than preventing remote server takeover.
We finally patched everything we could find.
Then our scanner discovered another PHP server.
Hostname:
TEMP-PHP-2014
Uptime:
4,512 days.
Nobody knows what it does.
Nobody owns it.
Nobody can shut it down.
But every time we block network access, the warehouse stops printing shipping labels.
Security has classified it as critical infrastructure.
It is running PHP 5.4.
The vulnerability has existed longer than half our employees.
The emergency patch took four hours.
Finding out what PHP actually runs took eleven.
The internet isn't held together with code.
It's held together with servers everyone is afraid to turn off.
Kevin Poireault retweeted

Re: the widely circulated blog claiming the PHP bugs aren't easily exploitable: @trailofbits has a working exploit that gets a shell on an unmodified MediaWiki installation.
eliastaylor.com/noexploit/

Kevin Poireault retweeted

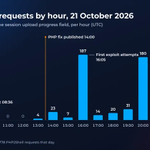
We're now seeing upload progress probes for PHP’s critical RCE vulnerability, CVE-2026-109618.
Our honeypots captured three HTTP requests from two source IPs, including PHP test code embedded in upload filenames.
Timeline (UTC):
• 20 Oct, 19:45: Previdian early-warning email sent.
• 21 Oct, 13:05: First attempt captured by our sensors.
• 21 Oct, 13:27: Follow-up warning emailed.
• 21 Oct, 13:30: PHP security fixes released.
• 21 Oct, 15:15: Previdian’s temporary virtual patch available.
Our initial warning preceded our first sensor observation by approximately 17 hours 21 minutes.
The evidence and IoCs:
• Observed source IPs: 166.1.90[.]109 & 43.134.82[.]85
• Multipart POST requests to /
• Fields: PHPSESSID and PHP_SESSION_UPLOAD_PROGRESS
• Two requests used the upload filename: <?php echo 1;?>.txt
Attackers did not manage to execute PHP or upload files in these first instances.
Update to PHP 8.2.35, 8.3.36, 8.4.27 or 8.5.12, or your vendor’s patched package.


Kevin Poireault retweeted

‼️ A critical Signal bug could keep your microphone, and possibly your camera, live after you hang up.
The other caller can flood the call's event queue so your hang-up is never processed.
Dubed CVE-2026-113380 it scored 9.3 and got fixed in September.


Kevin Poireault retweeted

PHP2Shell (CVE-2026-109618/109619) hit our MadPot honeypots on Oct 17, four days before disclosure.
Investigating? Start your timeline there, not at the advisory date. Patch to 8.5.12 / 8.4.27 / 8.3.36 / 8.2.35 now.
aws.amazon.com/blogs/securit…

Kevin Poireault retweeted

GitLab has patched a critical vulnerability rated CVSS 10.0 that could allow unauthenticated remote code execution on self-managed servers.
CVE-2026-110264 affects releases dating back to GitLab 7.0 in 2014.
If you self-host GitLab, check your version and upgrade to the fixed release. Even installations patched on October 12 may need another update.
A recent patch doesn't always mean you're covered.
🚨 CRITICAL: GitLab flaw (CVSS 10.0) affects 12 years of releases.
CVE-2026-110264 could allow unauthenticated remote code execution on self-managed servers.
Read - thehackernews.com/2026/10/cr…

Kevin Poireault retweeted
T'es adminsys et tu crois que ta journée est terminée ? Non mais allo quoi !
🚨 CRITICAL: GitLab flaw (CVSS 10.0) affects 12 years of releases.
CVE-2026-110264 could allow unauthenticated remote code execution on self-managed servers.
Read - thehackernews.com/2026/10/cr…
Kevin Poireault retweeted
Websites taken down across Europe ahead of critical cyber-security update bbc.in/4BgqGlW

Kevin Poireault retweeted

A cette heure, Orange n'a aucune visibilité sur un retour à la normale.
Selon les informations de BFMTV, la panne n'est pas liée à la faille PHP et le scénario de la cyberattaque n'est pas privilégié.
Il s'agit de la plus grosse panne d'Orange depuis 2012.
Kevin Poireault retweeted

The NCSC has issued an update to the PHP alert reflecting the release of mitigations.
We encourage UK organisations to take immediate action.
For more information on the issue as well as our guidance, head to⬇️
ncsc.gov.uk/news/critical-se…

Kevin Poireault retweeted
php2shell is the most consequential vulnerability I have ever helped discover. I am proud of how our team worked closely in coordination with the PHP Foundation to provide support and to harden the patch in preparation for this release.
Please read more about our approach:


OpenAI models helped researchers—operating as part of our Patch the Planet initiative—discover critical security flaws in PHP, an open-source programming language used to run an estimated 70% of websites.
Over the past two months, we led a coalition of maintainers, researchers, and security providers to prepare fixes and protections ahead of disclosure. This duration was necessary because the fix was quite intricate and required a major change to the PHP engine. Every site using PHP can now safely upgrade their version to stay secure, in addition to applying mitigations from various security vendors.
Due to the severity of these flaws and PHP’s widespread use, we consider this bug to be one of the most impactful vulnerabilities in recent memory. It also marks a new phase, where AI can find security bugs with internet-scale impact.
This is an example of the Defender’s Window in action: to our knowledge, frontier AI was able to find this vulnerability ahead of attackers, giving defenders time to prepare.
openai.com/index/coordinated…

Readers added context they thought people might want to know
OpenAI may claim a role in the coordinated response and patching process. But the initial discovery and exploit development, however, occurred several months earlier by an independent researcher.
x.com/lcfr_hax/statu…