

just a guy who is wandering the life
Melbourne, Australia
Joined August 2008
- Tweets9.2K
- Following123
- Followers4.6K
- Likes12.4K




Sonny Kieu retweeted

*sshole is out
if you run sshd on alpine, openwrt or any musl box with password auth on: update now
official writeup: sshhole.com

Sonny Kieu retweeted

Do you use Symfony, Laravel, Drupal, Doctrine or PHPUnit and want to upgrade them automatically?
You can forget the set crowds in rector.php
and use single method in Rector config instead ⬇️
getrector.com/blog/your-comp…

Sonny Kieu retweeted

Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.”
A significant blast radius.
This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression.
Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.

Sonny Kieu retweeted

Since we are all concerned with php2shell patch, let me share the fact that, like bugs, "patch for software" is also not a metaphor.
You know that ancient computers ran on punched paper tape and cards with one hole per bit of instruction.
If the code had an error, programmers had to physically cut out the flawed section, cover the hole pattern with a scrap of paper, and re-punch the correct code onto it.
This patched piece of paper is where the term "software patch" originates.
We still apply patches, just not on paper but hundreds or perhaps thousands of endpoints.


Sonny Kieu retweeted

Lot of #PHP snark going around right now from folks who've either never written software, or never done it in PHP (in the last 20 years).
I've architected, designed and hand-coded copious amounts of software in Java/Spring/Hibernate, .Net/C# Entity Framework and PHP/Symfony/Doctrine, applying very similar patterns and better practices of completely stack-agnostic concepts such as:
- Test-Driven Development (and given half-day and full-day hands-on live-coding workshops at conferences worldwide)
- Onion/Hexagonal Architecture
- Domain-Driven Design
- Data Mapper ORMs
Beyond workshops, I have spoken on these topics at conferences worldwide as well.
I might argue that I am not completely devoid of clue when it comes to these stacks' capabilities.
In fact, I have hired, coached and cross-trained engineers across these 3 stacks.
And I can assure you PHP shines within these paradigms, with an extremely vibrant, mature and robust ecosystem of Application Frameworks, Security Frameworks and Tools, and Open-Source Software Components and Libraries.
PHP is not WordPress. WordPress is not PHP. If you care about quality software, PHP is a great home for you. So is Java. So is C#. So are other languages. If you suck at software you'll suck in any stack. If you're good, each stack has strengths you can play to.
NOW let's talk about security.
This vulnerability, is the very first RCE to this level in PHP's history. It was reported back in August. AI did help. A lot. (Wiz claims one researcher did in a week what would previously have taken a team months)
Previous PHP RCEs had limited attack surfaces:
- 2024 - Windows CGI Only
- 2019 - One specific nginx setup
- 2012 - CGI only
None of which applied to reasonably-better practice typical Linux + Nginx + php-fpm deployments.
This right here was ... unique, I think even across any stack. The only language-runtime equivalent to it was probably Windows IIS Code Red.
That's not to say other stacks didn't have framework-level vulnerabilities with devastating impacts, if memory needs refreshed:
Ruby — Rails CVE-2013-0156: every Rails app, default config, pre-controller, botnet-exploited. The strongest analogue in any stack.
Java — Struts 2 CVE-2017-5638 (Equifax). Log4Shell needed the app to log attacker input; Spring4Shell needed WAR-on-Tomcat + JDK 9+ + POJO binding.
Node — React2Shell CVE-2025-55182 (Dec 2025, CVSS 10, CISA KEV): default create-next-app exploitable, but Express/Fastify/Nest untouched.
.NET — MS10-070 padding oracle (2010) leaked web.config/machineKey on every ASP (dot NET) site; RCE was a derived second step. Kestrel/ASP.NET Core has never had an RCE.
Look ... let's drop the snark. LLM-driven vulnerability research and breaching frameworks are about to humble the absolute heck out of all of us. They already have.
If you think your stack is not at risk, think again.
Sonny Kieu retweeted

‼️ BREAKING: Two leaked remote code execution flaws in PHP are real, watchTowr confirms.
PHP will ship fixes for two critical flaws, both rated CVSS 9.2, on Wednesday 21 October at 14:00 UTC, a day before the embargo was due to lift.
CVE-2026-109618 and CVE-2026-109619 first surfaced in a Hacker News post whose author admitted having no evidence beyond "source: trust me, bro".
Kevin Beaumont flagged the leak, and watchTowr confirmed it two hours later.
PHP says it may release sooner if details go public or exploitation appears. It has not named the CVEs or the affected versions.


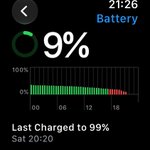
Upgrading from #AppleWatch SE2 to the new #ultra4 is a good decision. Battery life is such a great improvement. A full charge lasts more than 3 days with some facetime audio calls over cellular, indoor swimming, outdoor running/walking, and listening to music during exercise.

89
Sonny Kieu retweeted
Region: Near Leongatha, VIC
Mag: 4.8
UTC: 2026-10-02 16:01:39
Lat: -38.39, Lon: 145.87
Dep: 10km
For more info and updates, or if you felt this earthquake, go to earthquakes.ga.gov.au/event/…

Sonny Kieu retweeted

Preliminary notication from @GeoscienceAus is that a 4.8 magnitude earthquake with an epicenter near Leongatha occurred just after 2am.
By comparison, the September 2021 earthquake in Victoria was 5.9 magnitude.
Sonny Kieu retweeted

#Earthquake possibly felt 55 sec ago in #Australia. Felt it? Tell us via:
📱m.emsc.eu/#app
🌐m.emsc.eu
🖥emsc-csem.org
⚠ Automatic crowdsourced detection, not seismically verified yet. More info soon!

Sonny Kieu retweeted
We felt it too!
More earthquake information coming soon.
A reminder if you ever experience a major earthquake to Drop, Cover and Hold On.


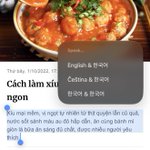
#iOS27 can no longer speak text in #Vietnamese. It incorrectly detects the text in Korean (?) for text-to-speech service, but correctly detects as Vietnamese for translation.


1
173
Sonny Kieu retweeted
If you're one of the 220 million people who flew to Vietnam between January 2017 and April 2026, your name, date of birth, sex, nationality, passport number, and travel details have been left exposed...
bleepingcomputer.com/news/se…


Sonny Kieu retweeted

CPU3命令でうるう年を判定する最適化。
bool is_leap_year_fast(uint32_t y) {
return ((y * 1073750999) & 3221352463) <= 126976;
}
A leap year check in three instructions
hueffner.de/falk/blog/a-leap…
GCCの実装でも取り入れられた。
github.com/gcc-mirror/gcc/co…