

Muslim | Astronomer | AI Red Teaming | F1 Fan 😉 🇵🇸
Joined June 2012
- Tweets10.6K
- Following589
- Followers1K
- Likes4.2K
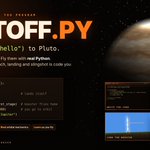




Launching a game I designed: "Liftoff.py"
Learn to code python by flying a rocket.
Code like NASA and explore the solar system.
Earn certificates.
So many things to do that also gain you real skills.
Available to play for free/download at: imshadab.itch.io/liftoff

M Shadab retweeted

The new bugbountyhunter site is *hopefully* going to be publicly released next month as I do some final touches, which means yes, zseano methodology v2 will be dropping before Christmas ;)
So much work has gone into this and I hope to continue helping people on their bb journey!
I found out about the Gray Swan Arena and AI Red Teaming
this time an year ago, and since then my life has changed. Thank you @GraySwanAI #GraySwanArena


M Shadab retweeted

"3 random dudes”
1. hacked apple, again and again.
httpvoid.com/Apple-RCE.md
httpvoid.com/Hello-Lucee!-Le…
httpvoid.com/Hacking-Apple-w…
2. your github enterprise is our github enterprise.
httpvoid.com/GitHub-Enterpri…
3. get a discord message from me, get pwned.
hacktron.ai/blog/discord-rce
youtube.com/watch?v=R3SE4VKj…
4. oh yeah, at one point we basically had shells across the electron ecosystem. check the DEF CON research.
media.defcon.org/DEF%20CON%2…
5. your supabase database is my database.
hacktron.ai/blog/supapwn
6. we got the posthog prod database.
hacktron.ai/blog/posthog-rce
7. react2shell? vercel paid us $170k for helping secure their waf.
hacktron.ai/blog/react2shell…
8. your palo alto vpn is my vpn.
hacktron.ai/blog/cve-2026-02…
9. ai ides? we got shells for you, antigravity
hacktron.ai/blog/hacking-goo…
10. windsurf rce.
youtube.com/watch?v=23Mz7qcR…
11. turning cluely into malware.
hacktron.ai/blog/hacking-clu…
12. ai browsers? sure, uxss: your perplexity browser is my browser.
hacktron.ai/blog/perplexity-…
13. openai atlas too. kinda uxss
hacktron.ai/blog/hacking-ope…
14. hey, it’s not even our first time hacking discourse.
projectdiscovery.io/blog/dis…
15. adobe coldfusion: pre-auth rce. because apparently we needed another one.
projectdiscovery.io/blog/ado…
there’s a lot more. go dig.
anyway, yes: “3 random dudes.”
and @HacktronAI is full of more random dudes like these.

M Shadab retweeted
I built a new home for my book, JavaScript for Hackers.
Every payload on the page is real. Click one and it pops in your browser.
Then learn to build your own: parenthesis-free calls, non-alpha JS from just !+[]{}, DOM clobbering, SOP bypasses, the latest XSS. 1/4

M Shadab retweeted

$3,700 Anthropic bounty for breaking Claude Code’s sandbox with one clever .git trick
CVE-2026-55607 High (CVSS 7.7)
Claude Code allowed creation of worktrees named .git. Combined with:
- Symlink following in worktree tools
- Git fsmonitor hook execution
- zsh sourcing ~/.zshenv before seatbelt sandbox
Full unsandboxed RCE via prompt injection.
This is next-level: Prompt injection on .git worktree confusion symlink to $HOME to write to ~/.zshenv before sandbox kicks in.
If you’re using Claude Code, update to v2.1.163 right now.
M Shadab retweeted

❗️ An Israeli startup founder secretly uploaded a cluster of malicious typosquatted npm packages that impersonate Anthropic, Vercel, LangChain, Ollama, OpenAI and Aspect Security and profile developer machines on install.
The packages skip passwords and tokens by design. Instead, the install script harvests identity: hostname, every git and SSH email on the box, teammate emails from the git reflog, AWS/GCP profile and account details, and the corporate DNS domain, all shipped to a Google Cloud Run endpoint.
There were about 20k downloads before takedown.


M Shadab retweeted

He who exalts himself will be humbled !
There’s levels in this game!
Congratulations Justin, you deserve this belt more than anyone!


Hacked 384 AI Models to get $250 in the Staged Attack competition of @GraySwanAI Arena!
#airedteaming #aisafety #bugbounty


Got my first AI Red teaming win with a bounty of $500 on the Gray Swan Arena.
It was the Indirect Prompt Injection arena, the top20 were winners in individual waves and top40 in overall.
I managed to break 338 models and secured top20 in wave 1 and top40 in overalls.

